-
Key: RAAML12-15
-
Status: closed Implementation work Blocked
-
Source: MITRE ( Ms. Mary Tolbert)
-
Summary:
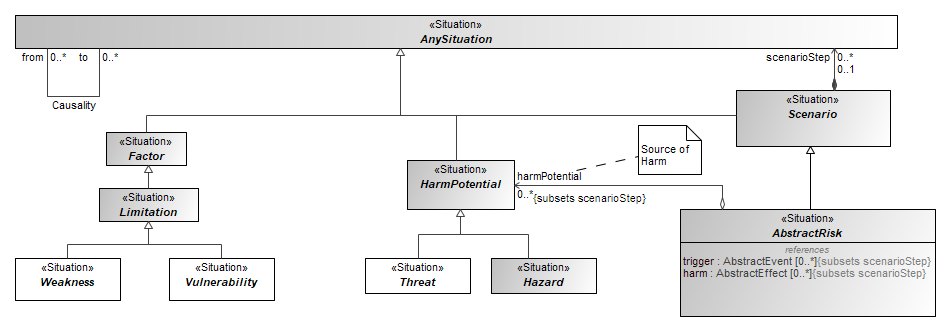
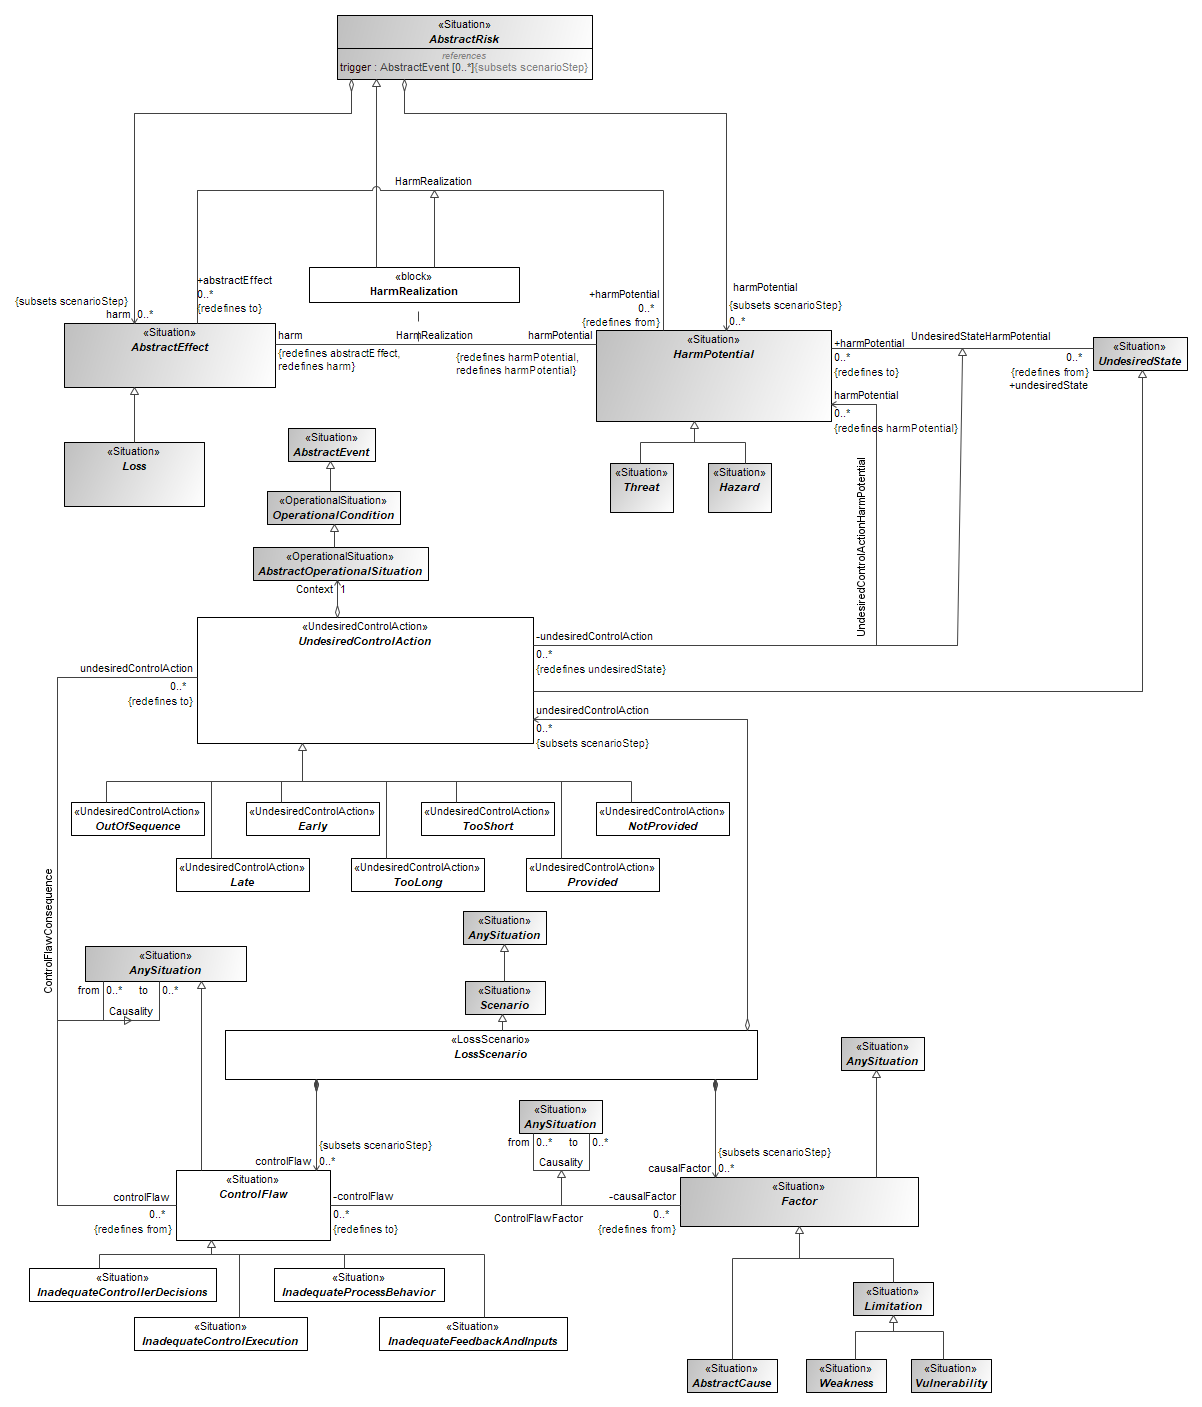
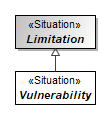
The issue is that Vulnerability is not currently stereotyped as Vulnerability, and is not marked as Abstract, which puts it out of alignment with the other RAAML library elements. To resolve this, the ticket calls for stereotyping it as Vulnerability and marking it as abstract. This change should help ensure consistency with Factors and Limitations in the STPA Loss Scenario
-
Reported: RAAML 1.1 — Tue, 24 Mar 2026 13:54 GMT
-
Disposition: Resolved — RAAML 1.2b1
-
Disposition Summary:
*Partial resolution to make Vulnerability abstract for 1.2 *
Per the RAAML RTF 1.2 working meeting it was decided to partially resolve this issue by updating the Vulnerability to be abstract for 1.2 and defer the addition of the Vulnerability stereotype to 1.3. A new issue will be created for the Vulnerability stereotype addition.
-
Updated: Thu, 17 Sep 2026 01:17 GMT
-
Attachments:
- GeneralRAAMLSecurityLib.zip 1 kB (application/zip)
- GeneralSecurityConceptsLibrary.png 42 kB (image/png)
- STPALibrary.png 126 kB (image/png)
- Vulnerability.png 3 kB (image/png)
RAAML12 — Vulnerability is not currently stereotyped as Vulnerability, and is not marked as Abstract,
- Key: RAAML12-15
- OMG Task Force: Risk Analysis and Assessment Modeling Language (RAAML) 1.2 RTF